Skip to content
Start awareness training for free | 4 colleagues
RGPD
Security awareness training for NGOs

A training programme for your NGO

From headquarters to the newest office, every colleague learns the same good habits.

Copenhagen Stockholm Berlin Paris Geneva Rome Madrid Lisbon New York Nairobi
  1. 0

    Social economy organisations1
  2. 0

    People working in them1
  3. 0

    Had cyber security incidents2
Localised training

Target your awareness training

Segment awareness training for each location or team.

CopenhagenHeadquarters
96%
BerlinCountry office
91%
ParisCountry office
88%
GenevaCountry office
84%
MadridCountry office
79%
LisbonNew this year
62%
Charities in numbers

NGOs are behind on training

0

Most boards call it a priority, but few have trained their staff yet.

60% of NGOs say cyber security is a priority for their leadership, but in 2025 only 17% had trained their staff in the past year.2

For your board

A management report

Download a training report you can show your board and your donors.

  • An organisational certificate
  • A training log
  • Up to date
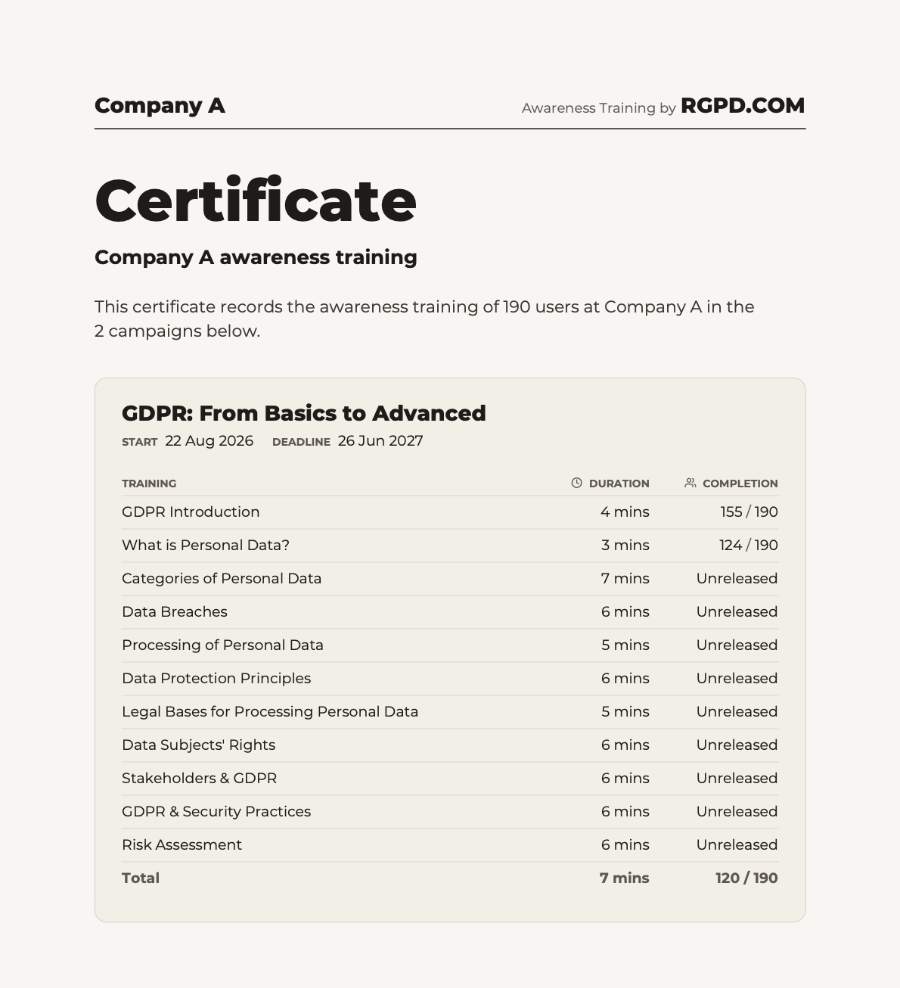
An organisational certificate from RGPD.COM: the campaign, each training and how many people completed it
From the same survey
0

28 in every 100 NGOs had a breach or an attack last year.

87% of these NGOs were hit by phishing.2

Awareness training for everyone in your NGO

Staff, volunteers and consultants

Staff

Train the staff who handle your donor lists, member records and payroll.

Volunteers

Group your volunteers and choose the courses that fit the data they see.

Consultants

Include external consultants in your training plan with a campaign of their own.

Features

Campaigns for every office, training for every colleague and a report for your board.

See every feature
Prices Free for 4 users

Prices for NGOs of all sizes, from a small local team to an organisation with offices in many countries.

See prices
Free version

Start free for 4 users

Help your team recognise phishing and handle personal data with confidence. Choose a topic and plan your first security awareness training campaign.

Compliance Hub

The paperwork, done properly

The documents you shouldn't have to ask for, ready for your records before you even sign up.

EU by design

The company
EU owned
Data processors
EU owned
Your data
EU storage
Agreement Terms & Conditions 1. Parties1.2 The Agreement between The Provider and the Customer consists of the order confirmation, if any, any related appendices, and these CUSTOMER TERMS AND CONDITIONS, including the Data Processing Agreement. In the event of any inconsistencies between the order confirmation and the CUSTOMER TERMS AND CONDITIONS, the provisions of the order confirmation shall prevail. Agreement Data Processing Agreement For the purposes of Article 28(3) of Regulation 2016/679 (the GDPR)1. Preamble1) These Contractual Clauses (the Clauses) set out the rights and obligations of the data controller and the data processor, when processing personal data on behalf of the data controller.2) The Clauses have been designed to ensure the parties’ compliance with Article 28(3) of Regulation 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data and repealing Directive 95/46/EC (General Data Protection Regulation). Appendix A Information about the processing A.1. The purpose of the data processor’s processing of personal data on behalf of the data controller is:Personal data will be processed on behalf of the Data Controller to deliver successful awareness training via an E-learning platform.A.2. The data processor’s processing of personal data on behalf of the data controller shall mainly pertain to (the nature of the processing): Appendix B Sub-processors The following table shows our vendors used to process personal data on behalf of the data controller.Name | Business ID. | Address | Purpose Appendix C Security Measures Risk ManagementRGPD.COM regularly assesses the risks to its systems and the personal data they process. This assessment is informed by the latest threat landscape and new industry insights, which shape our security measures and initiatives.Information Security PoliciesRGPD.COM follows an IT security policy, which is regularly reviewed to ensure compliance. Management approves the policy, which is communicated to all relevant employees and partners. It is reassessed regularly and whenever significant changes occur. Policy Privacy Policy ControllerWe are data controllers as we process the personal data of our customers and partners. You will find our contact information below.If you have questions about processing your data, you can contact us via mail@rgpd.com.Processing Activities Policy Cookie Policy This website does not set cookies and stores nothing on your device.You can learn more about how we process personal information in our privacy policy.