Skip to content
RGPD
Security Awareness Training Platform

Awareness Training

GDPR ISO27001 NIS2 AI Act CIS18 NIST-CSF

Serious training. Seriously simple.

  • Become compliant with the GDPR, NIS2, and more.
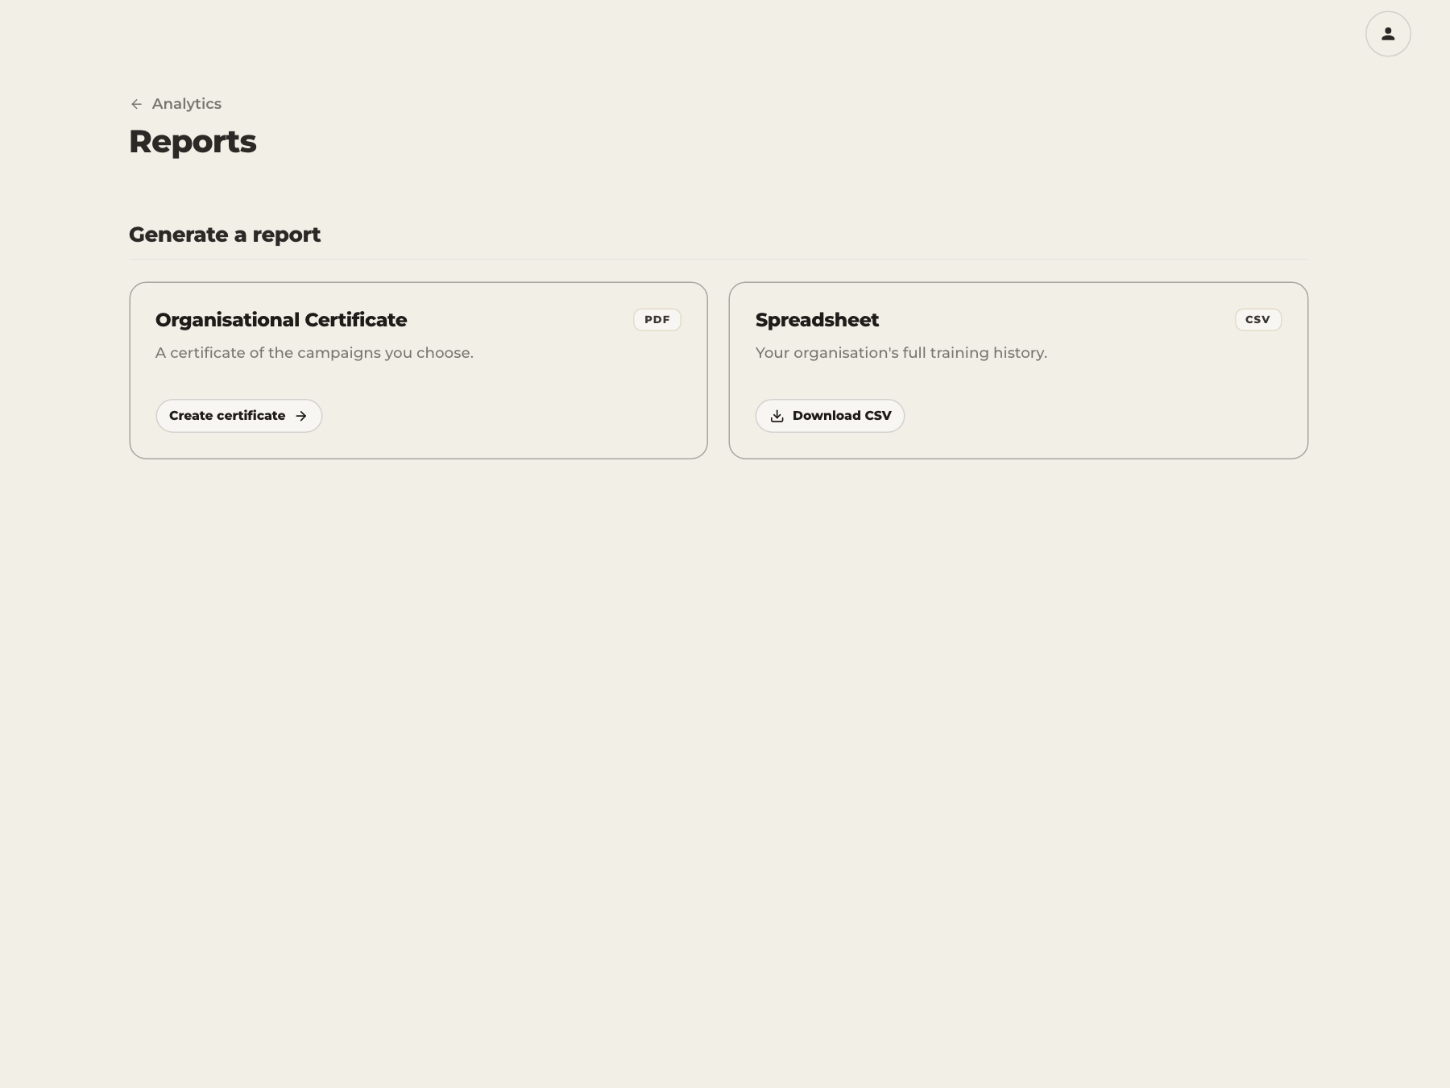
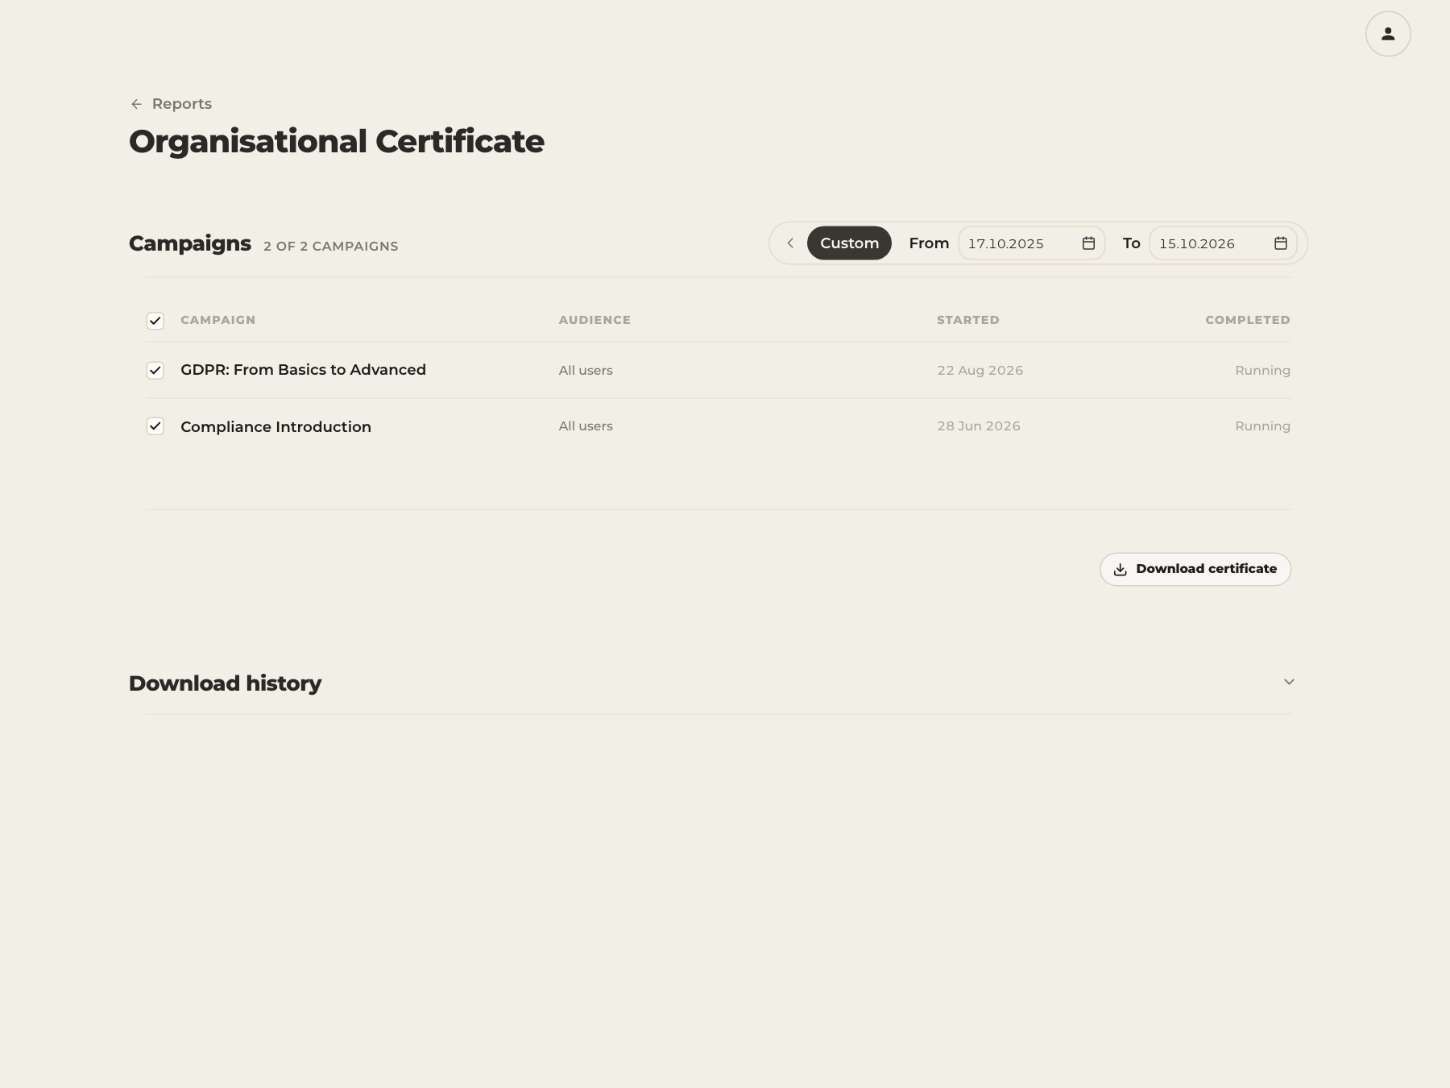
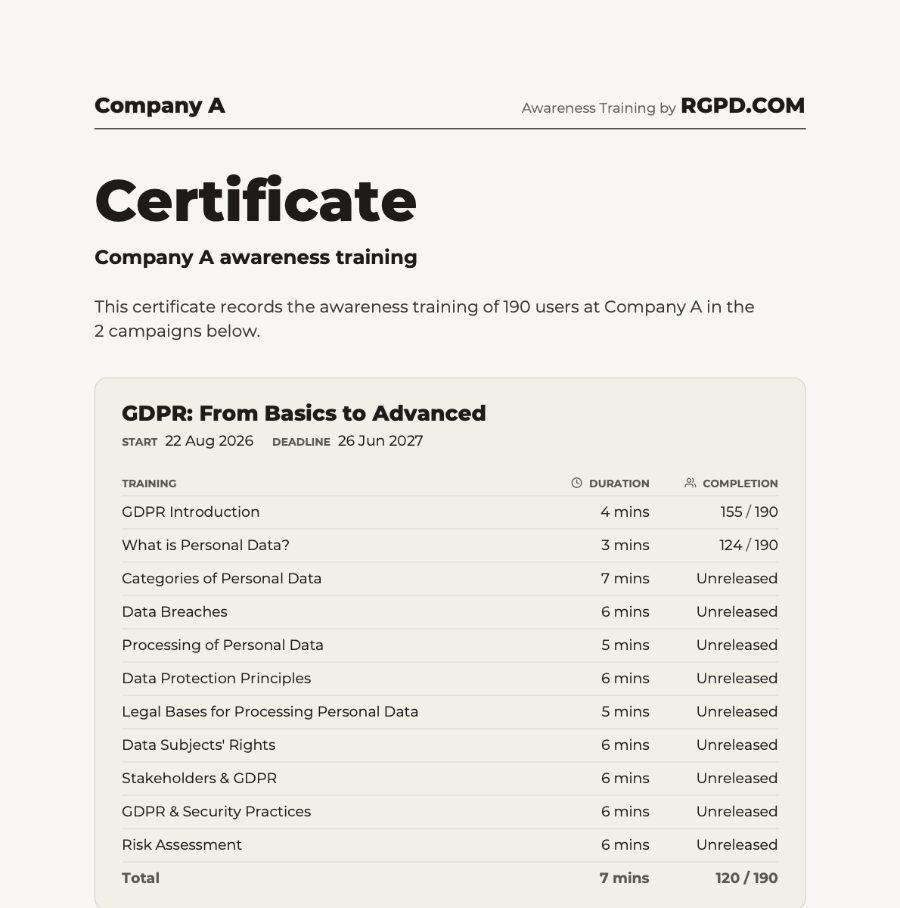
  • Certificates, documentation, and compliance.
  • 60+ high-quality micro-lessons.
Short videos

The numbers behind awareness training

Training requirements

Compliance includes your people

The safest systems still depend on the people who use the systems every day.

Tasks of the data protection officer

1. The data protection officer shall have at least the following tasks:

(b)… including the assignment of responsibilities, awareness-raising and training of staff involved in processing operations, and the related audits;

Governance

2. Member States shall ensure that the members of the management bodies of essential and important entities are required to follow training, and shall encourage essential and important entities to offer similar training to their employees on a regular basis, …

AI literacy

1. Providers and deployers of AI systems shall take measures to support the development of AI literacy of their staff and other persons dealing with the operation and use of AI systems on their behalf, …

Compliance Introduction Training

Short introductions to GDPR, NIS2 and information security. Done before lunch, remembered long after.

3 lessons, 4 minutes

GDPR Introduction

What the GDPR is, why it exists and who must follow it.

See the course

3 lessons, 6 minutes

NIS2 Introduction

Who NIS2 covers, what it asks for and what management answers for.

See the course

3 lessons, 6 minutes

Information Security

What information security is and what it means in everyday work.

See the course
The platform

The platform to train your organisation

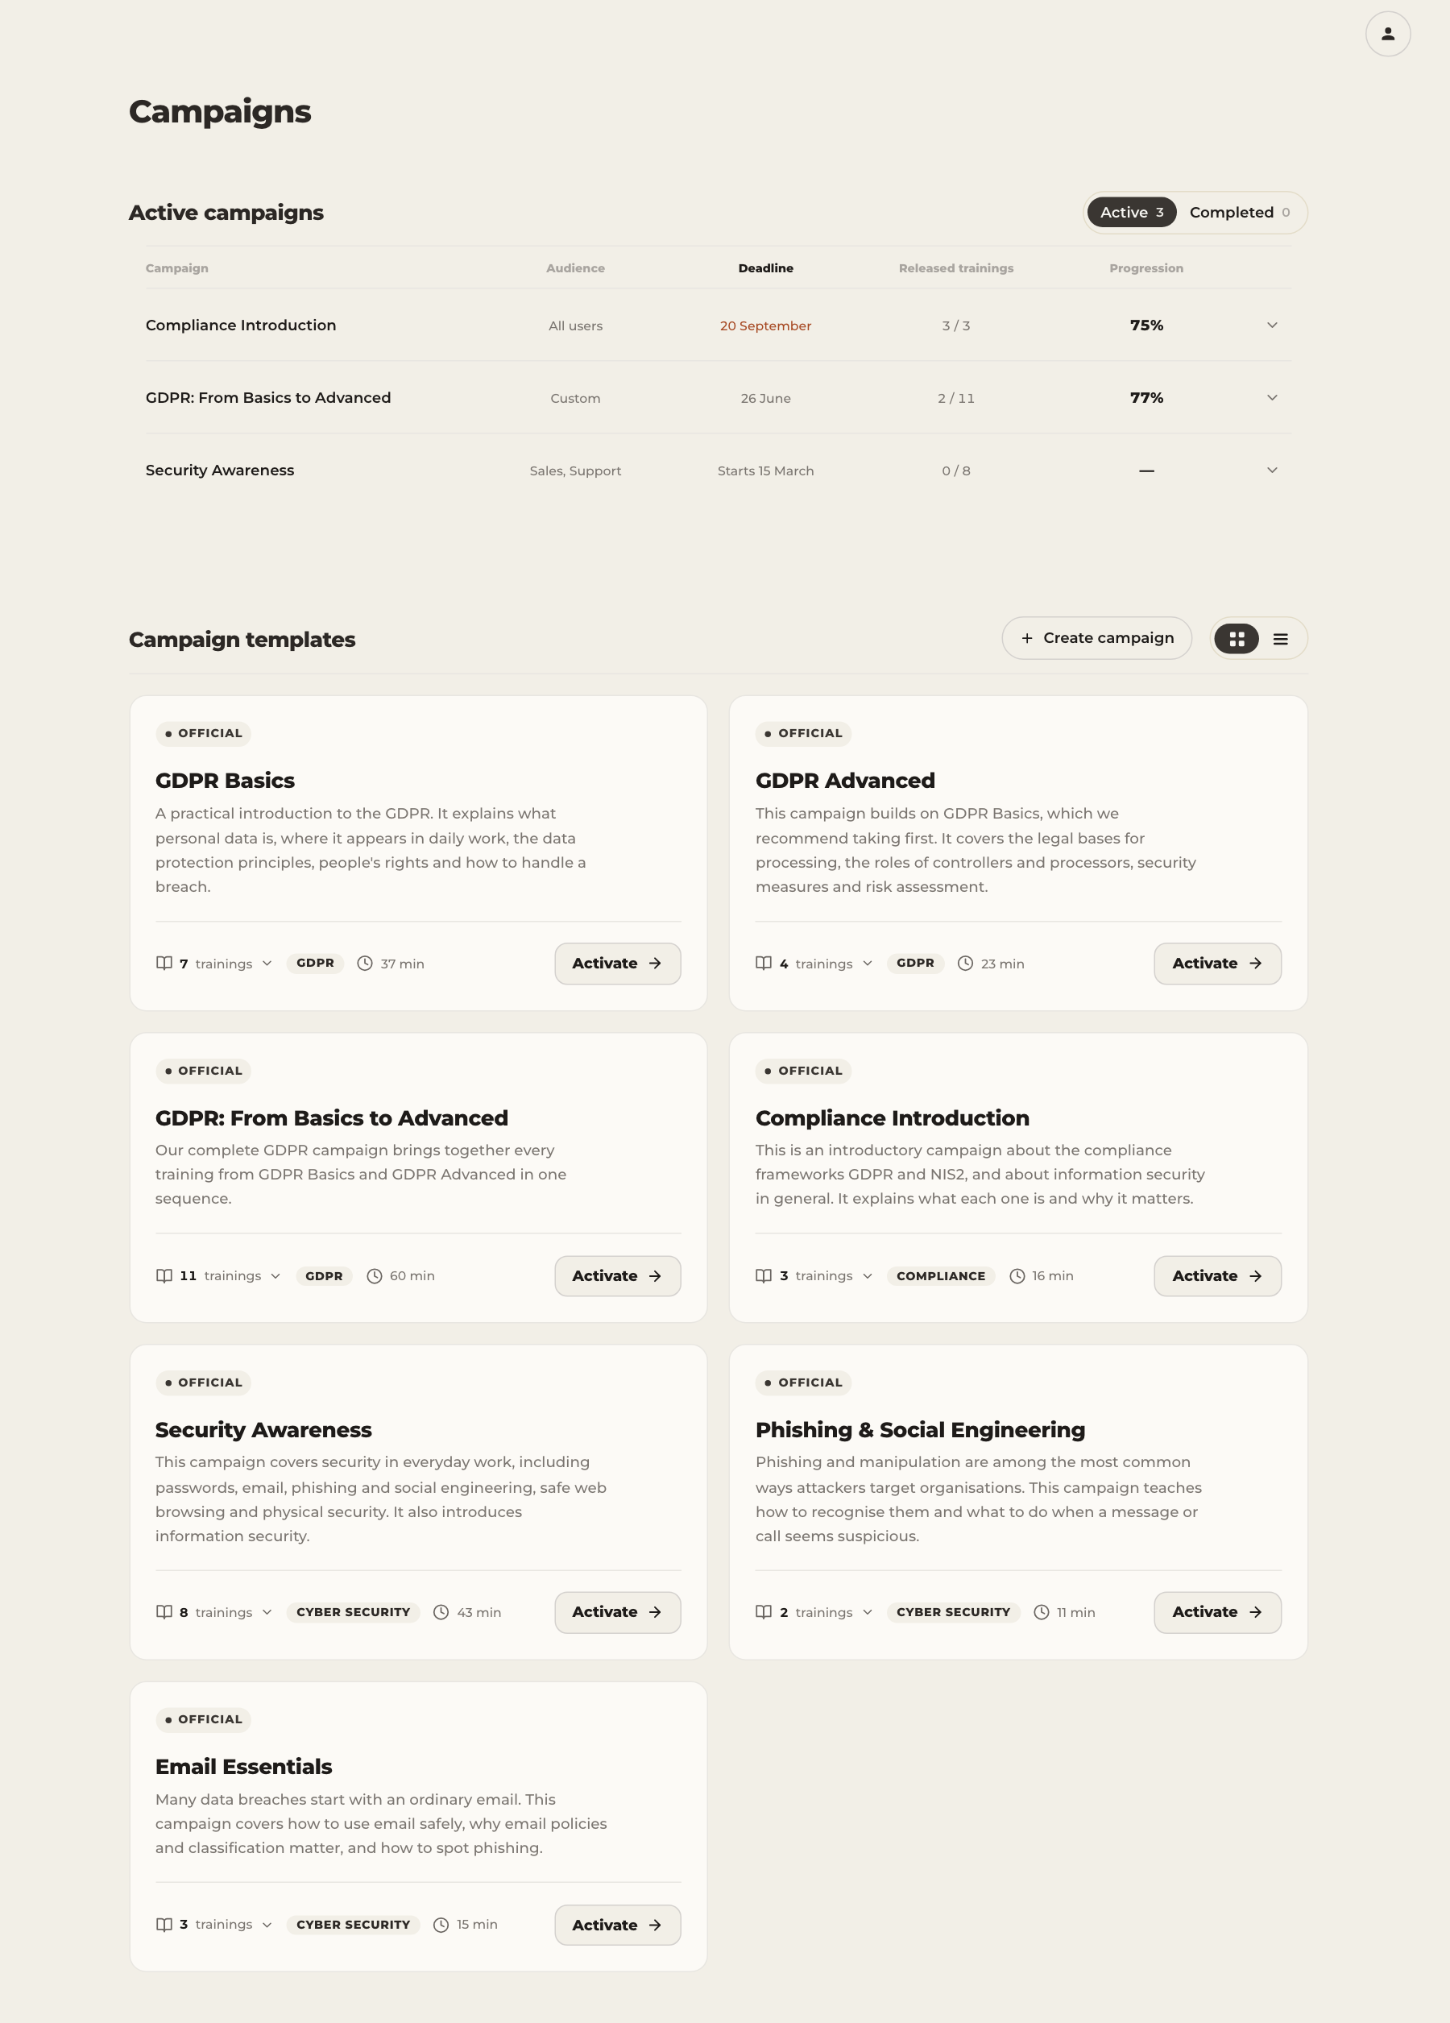
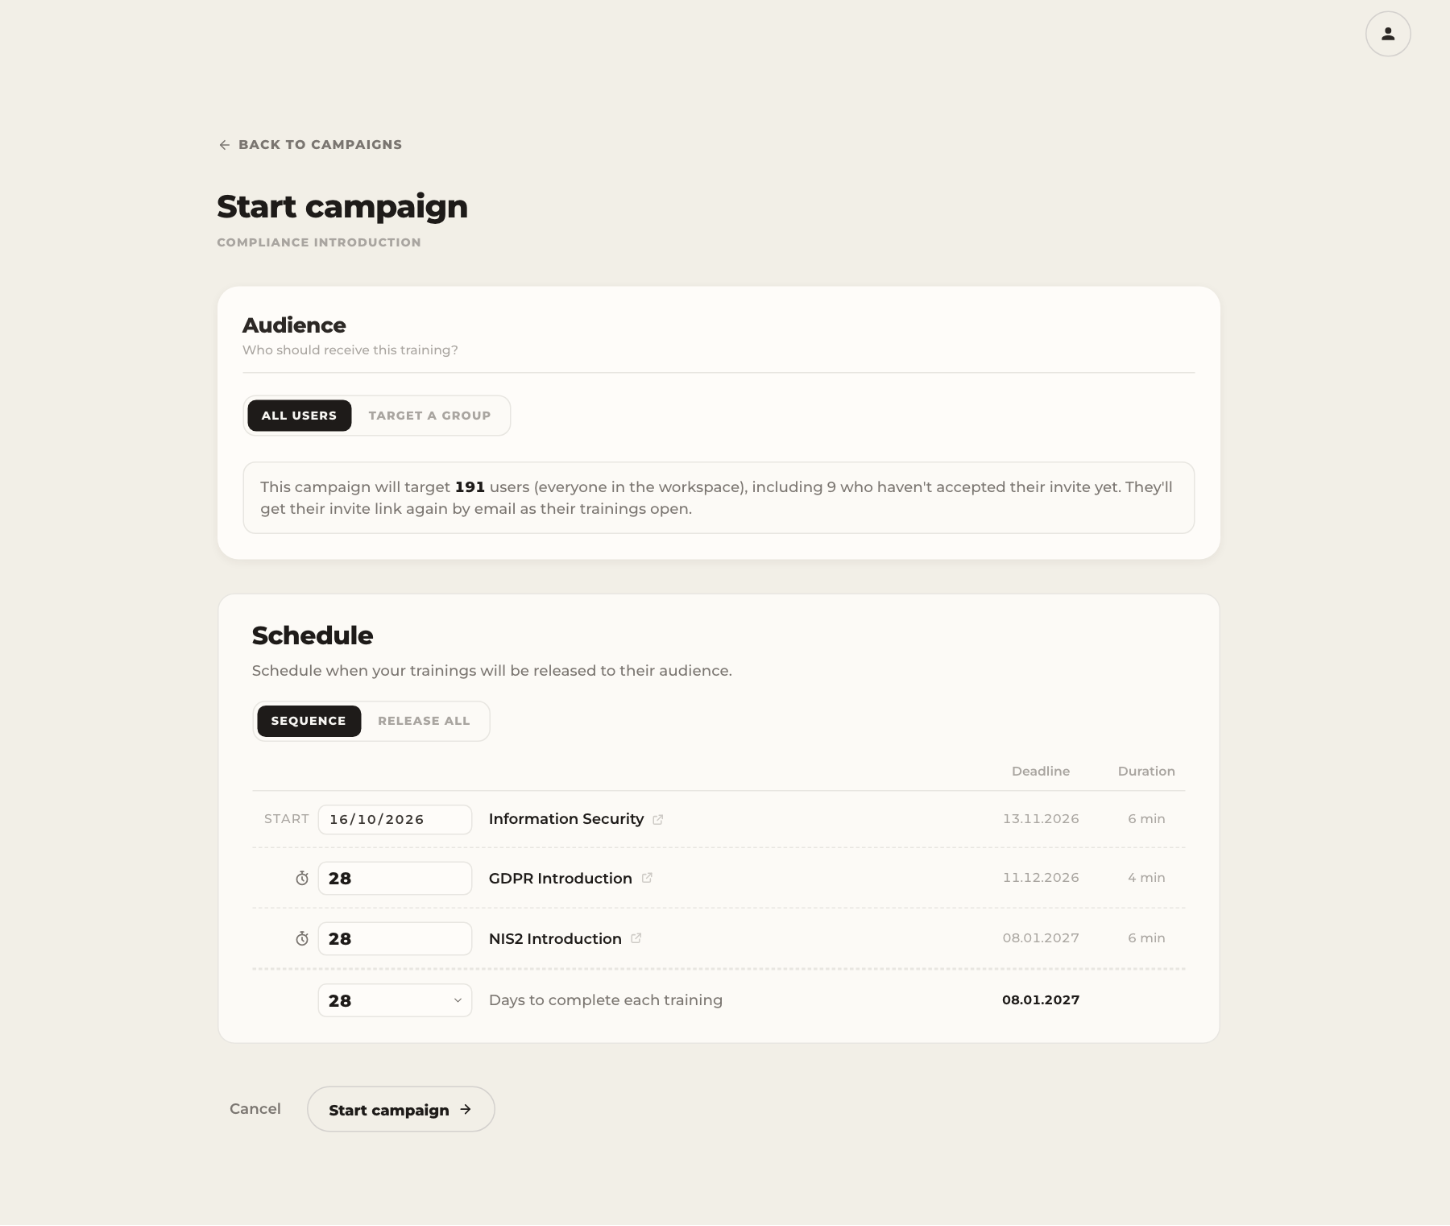
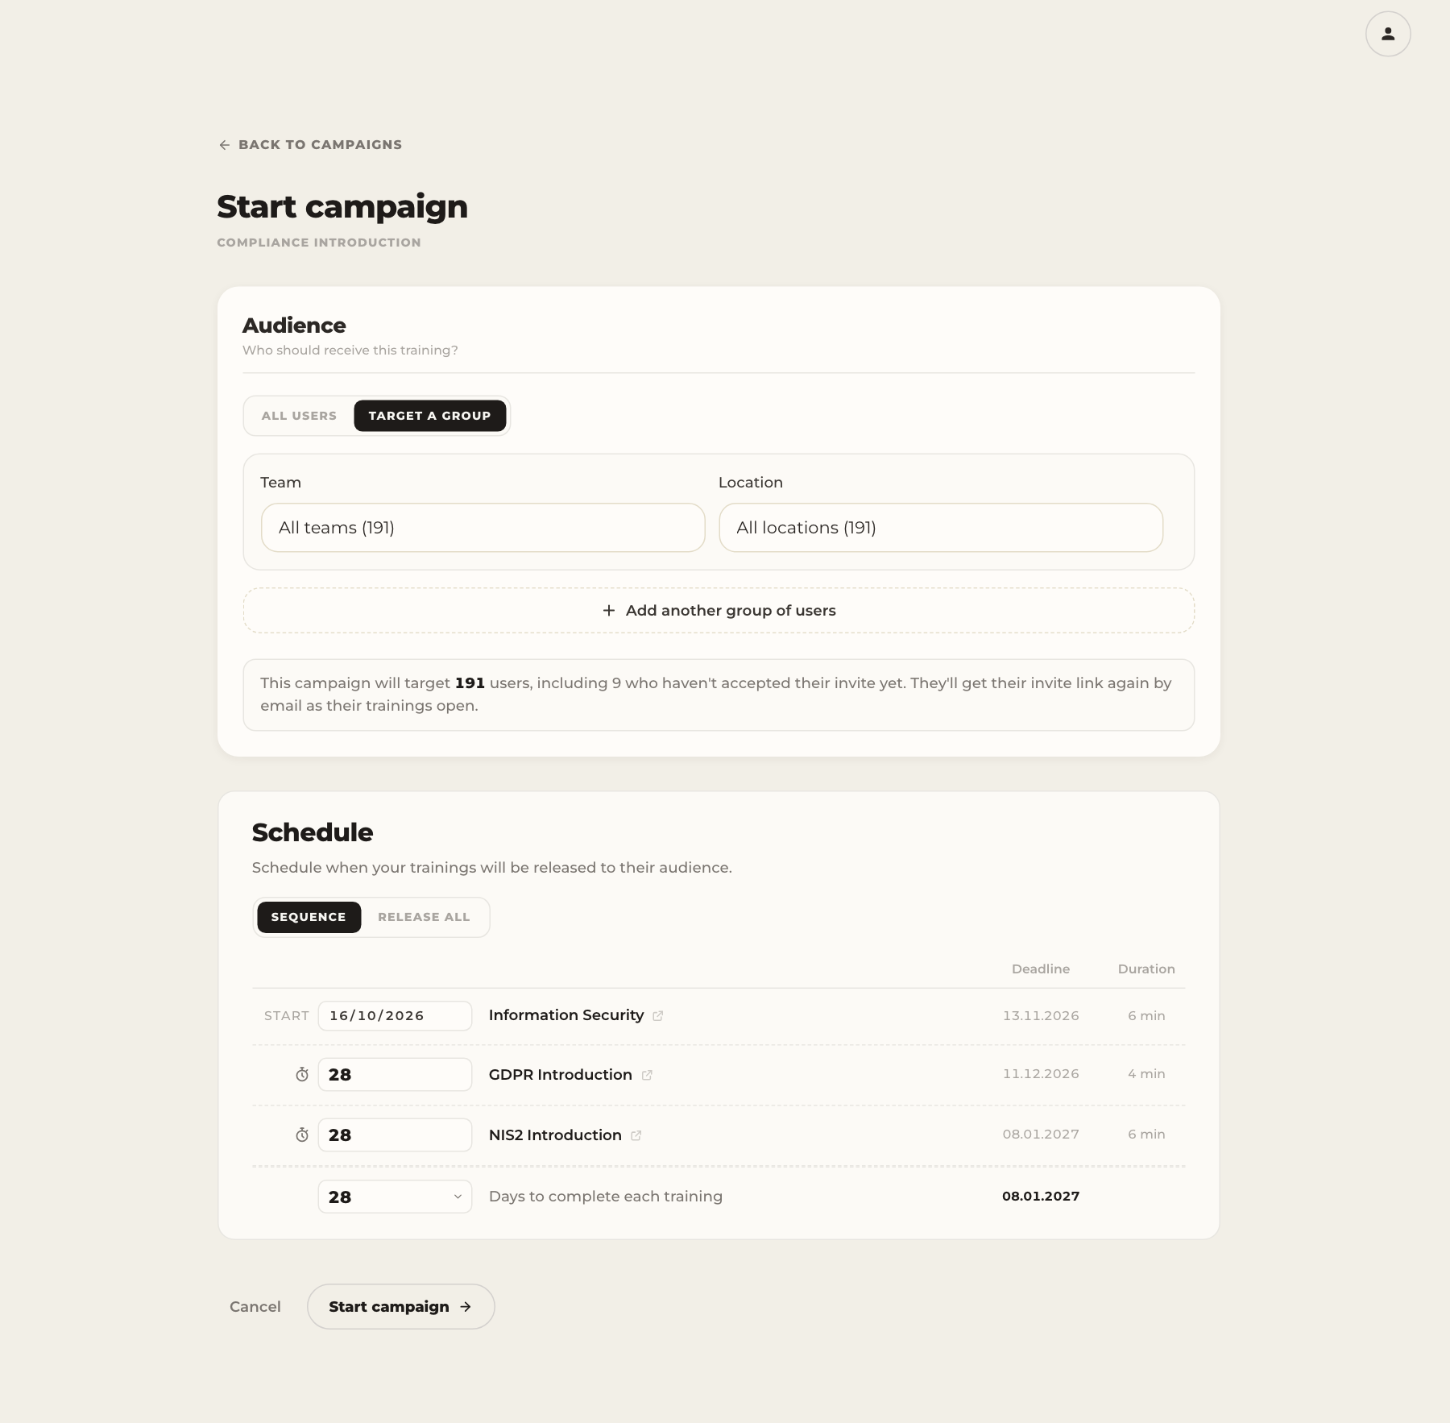
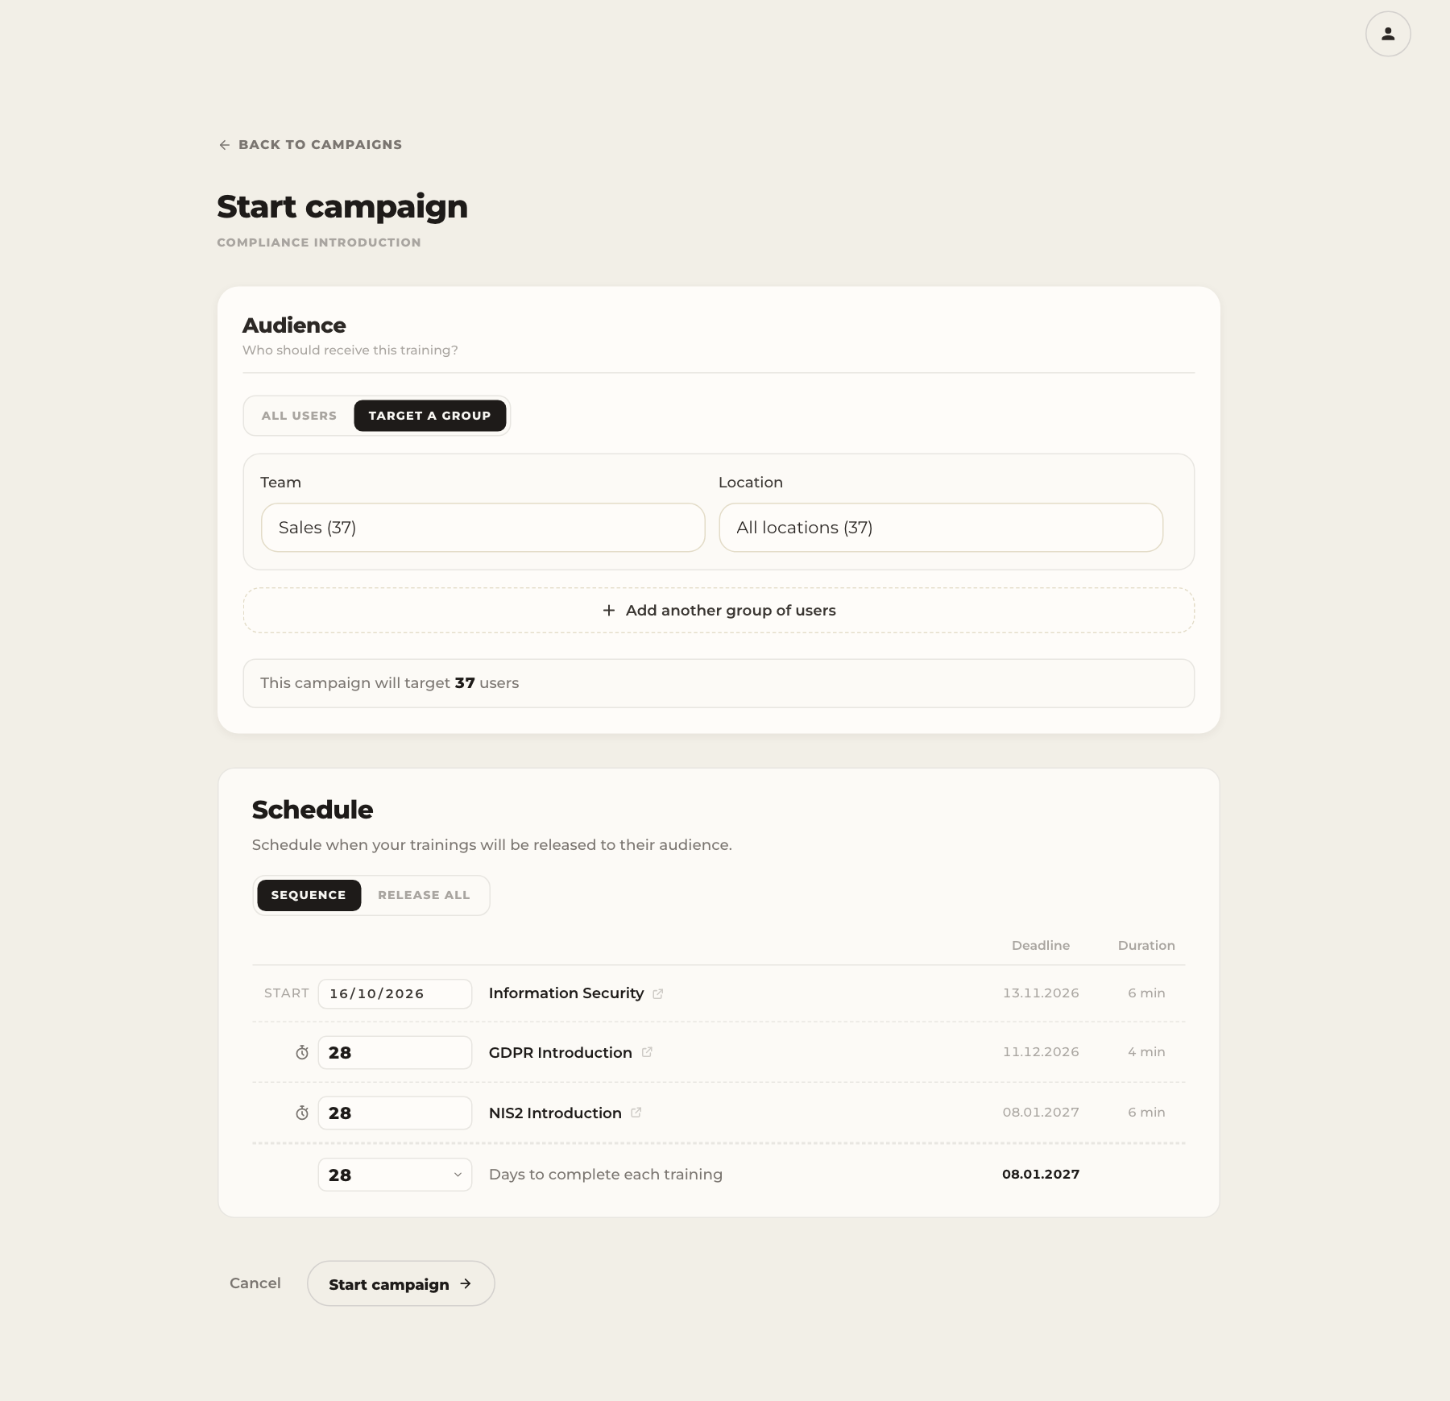
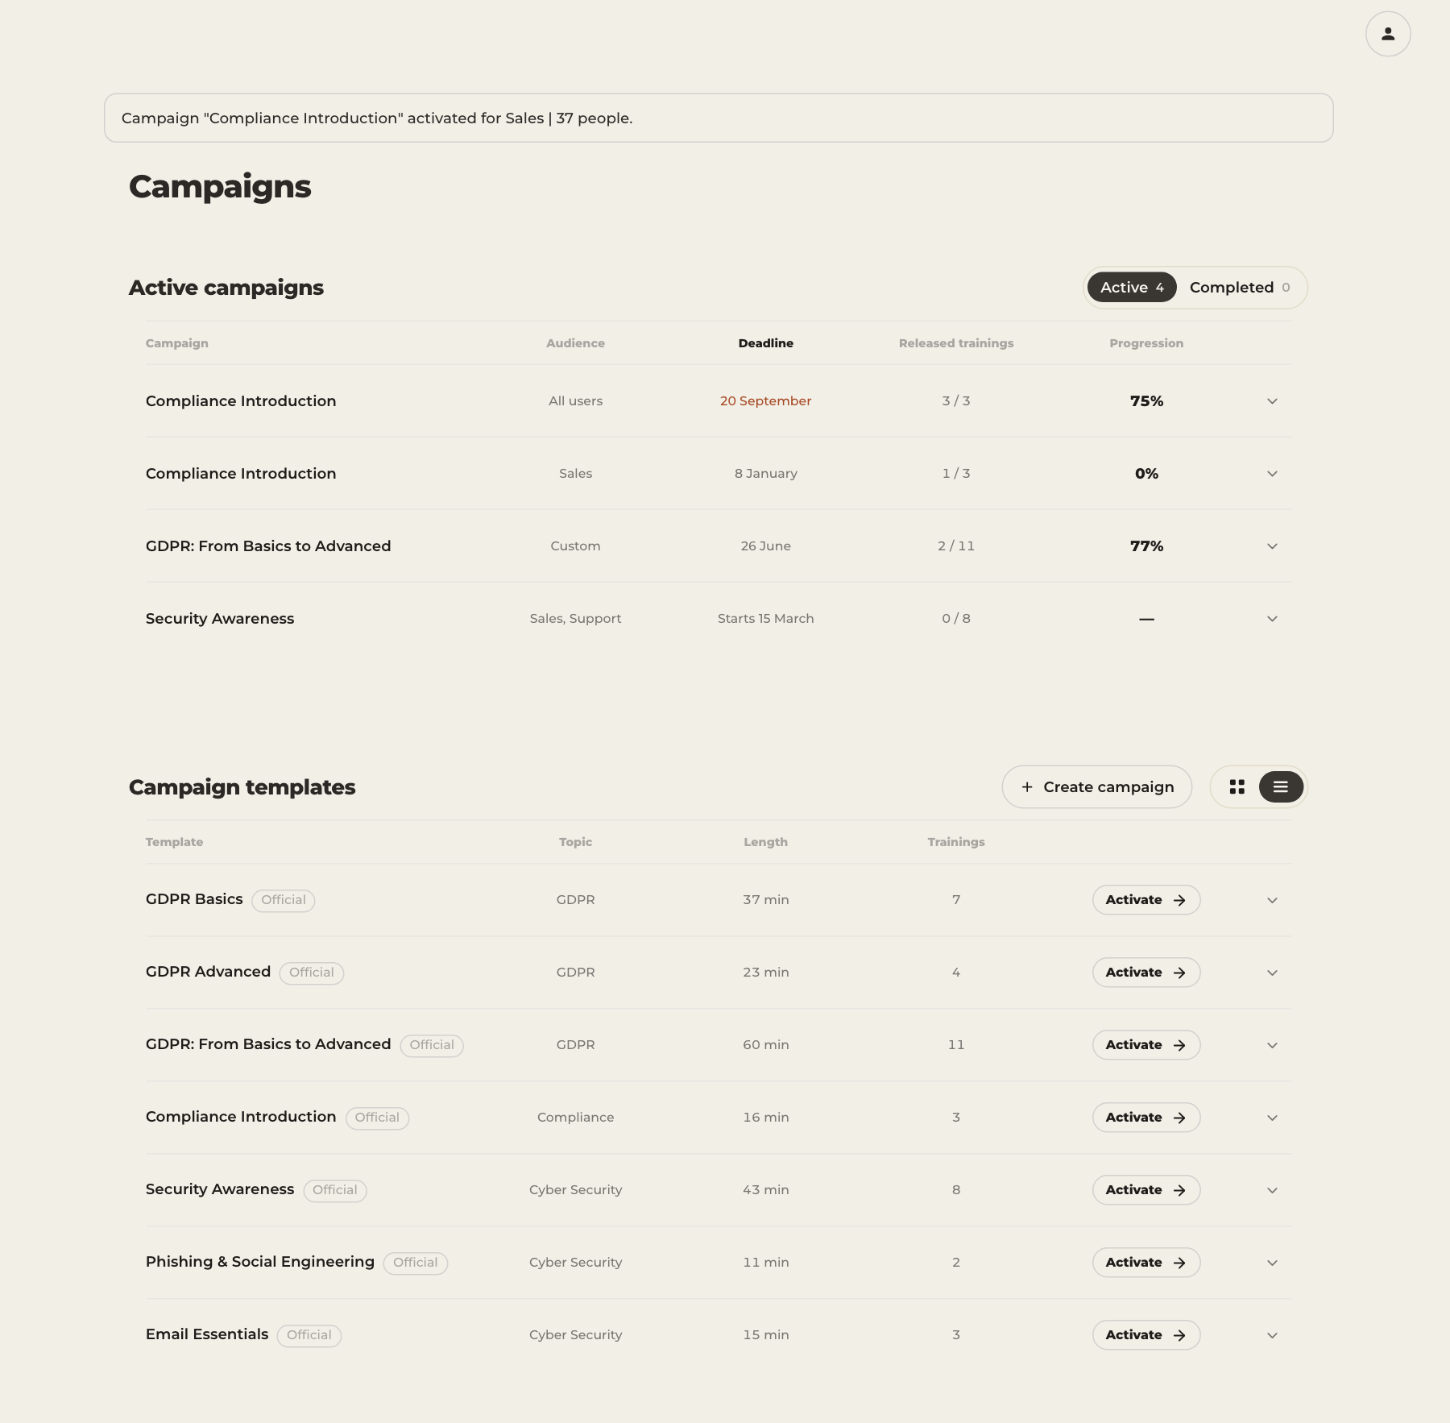
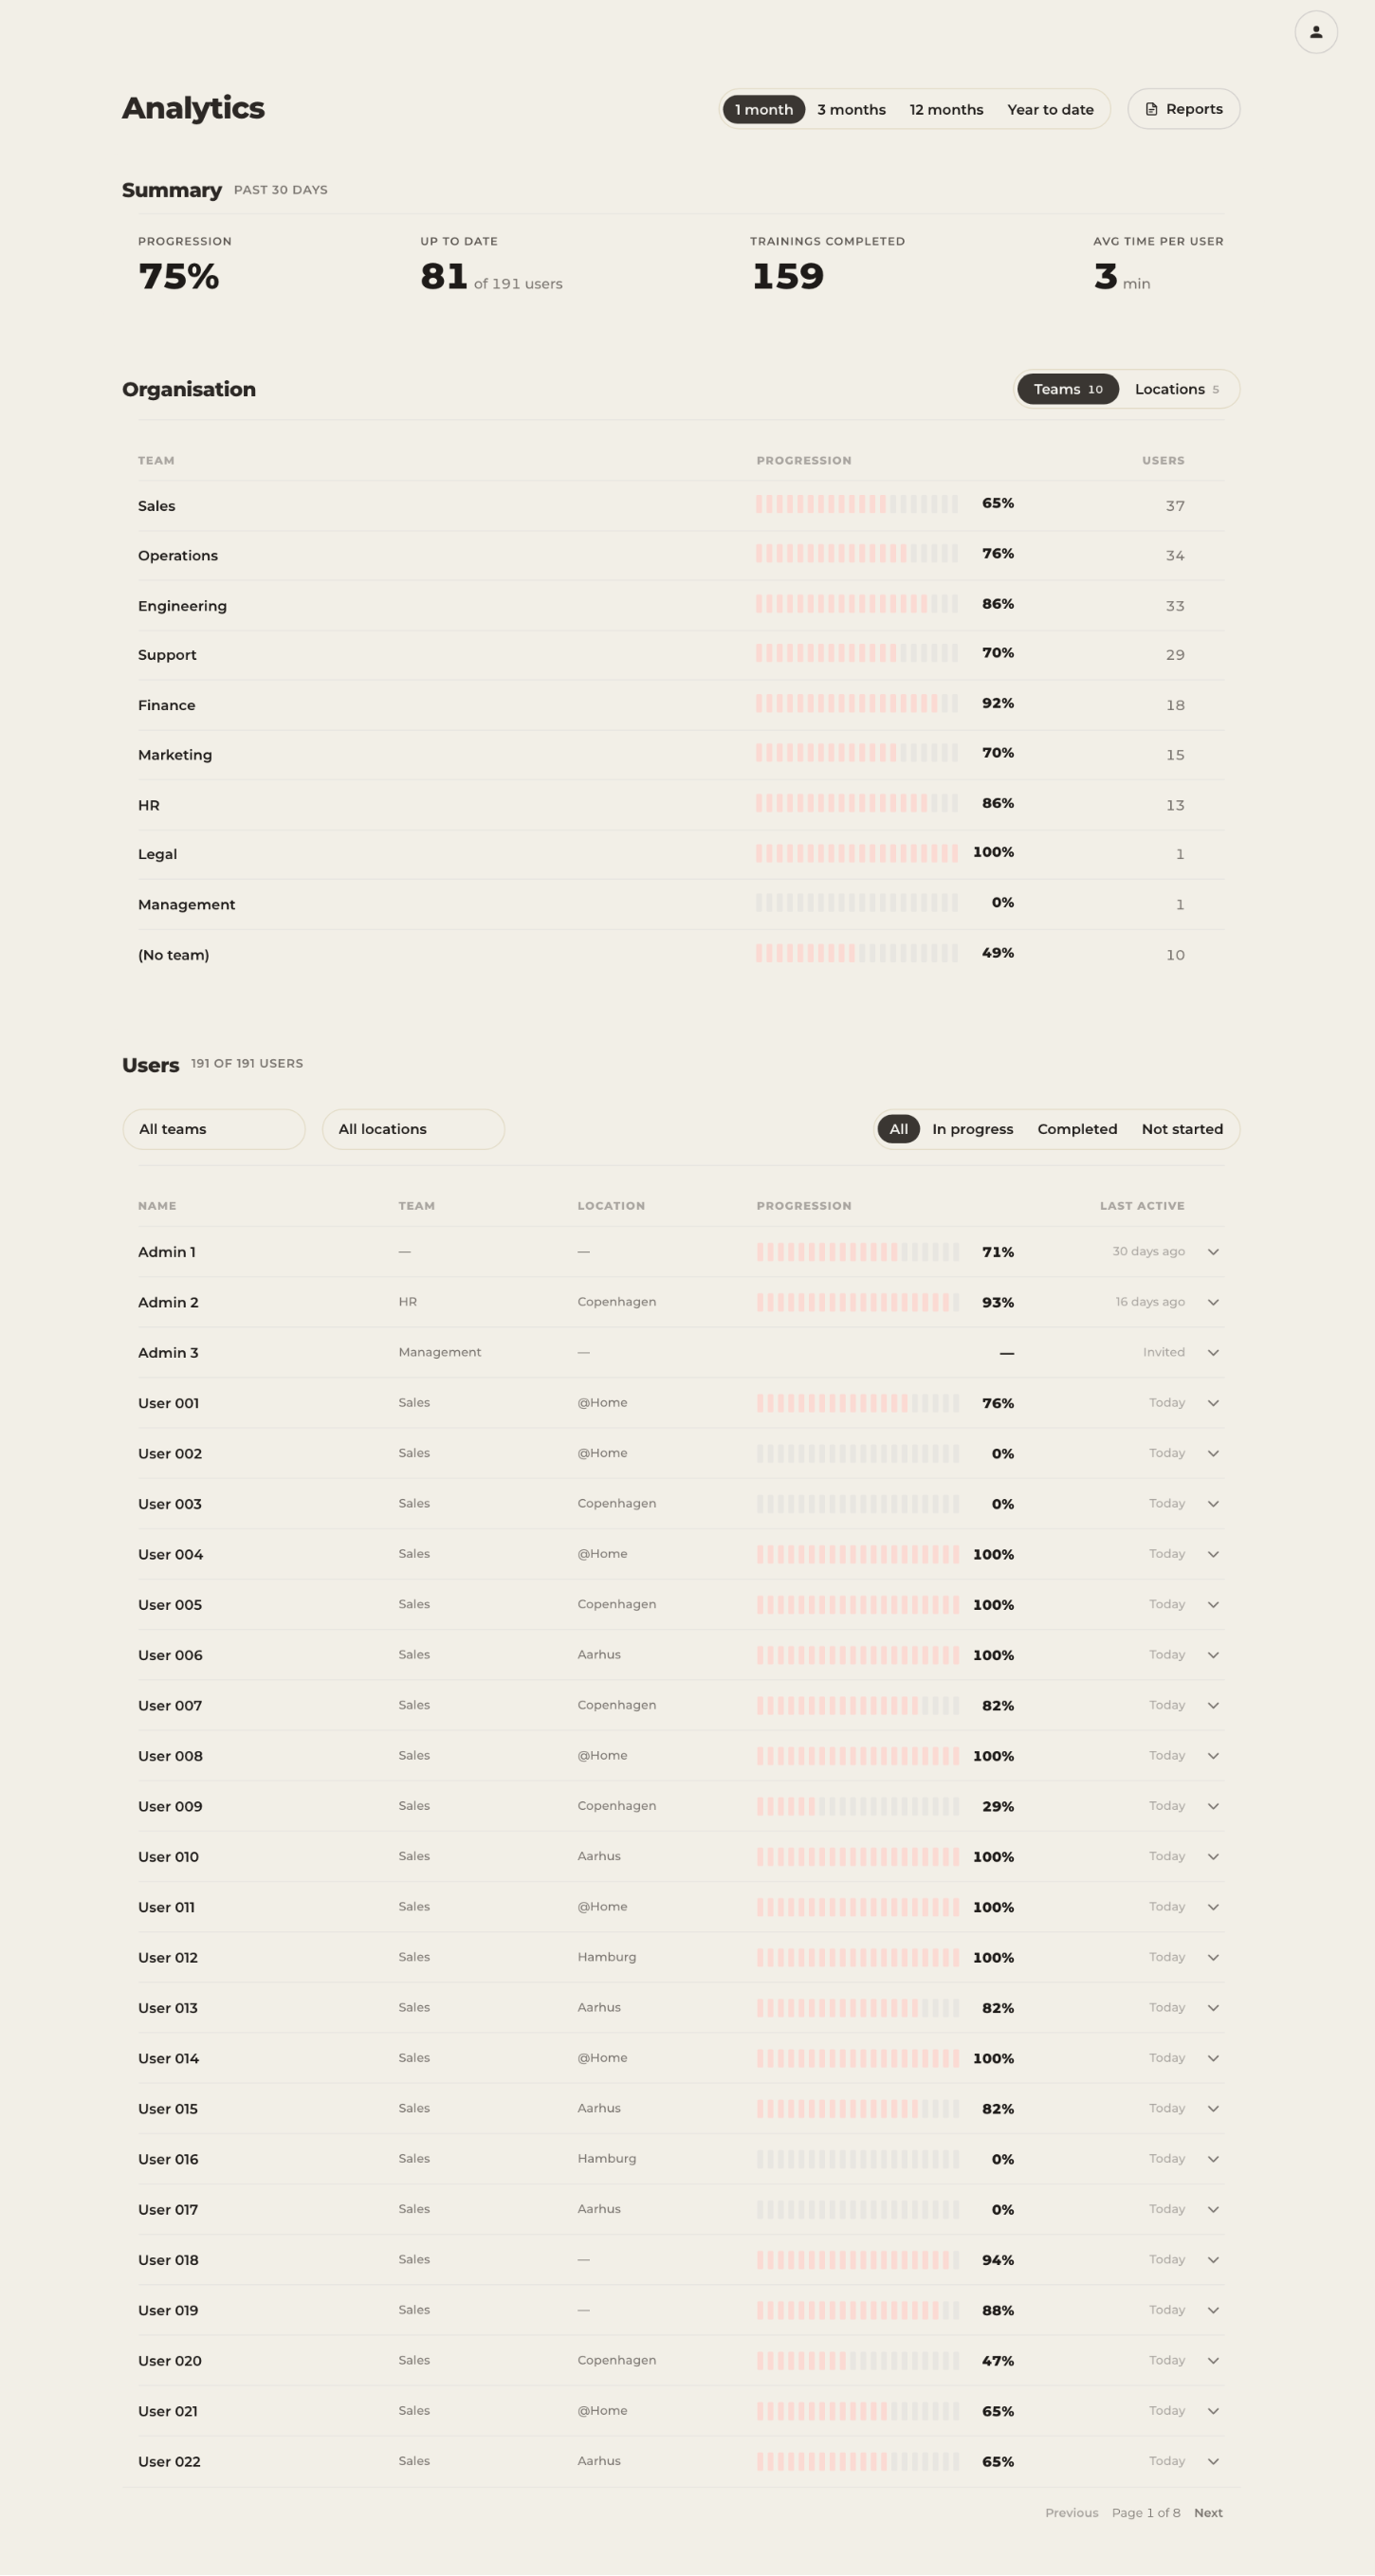
You choose what, who and when. The platform sends each training and its reminders, and records every completion for your certificate.
IT Security Frameworks Overview
IT Security

Security Frameworks Training

  • Train your team on industry-standard security frameworks including ISO 27001, CIS18, and NIST-CSF to strengthen your organisation's security posture.
  • Practical awareness training that helps employees understand and apply security controls in their daily work.
Free templates

Templates for your compliance documentation

Start from a ready-made template instead of a blank page, and make it your own.

All templates

Compliance Hub

The paperwork, done properly

The documents you shouldn't have to ask for, ready for your records before you even sign up.

EU by design

The company
EU owned
Data processors
EU owned
Your data
EU storage
Agreement Terms & Conditions 1. Parties1.2 The Agreement between The Provider and the Customer consists of the order confirmation, if any, any related appendices, and these CUSTOMER TERMS AND CONDITIONS, including the Data Processing Agreement. In the event of any inconsistencies between the order confirmation and the CUSTOMER TERMS AND CONDITIONS, the provisions of the order confirmation shall prevail. Agreement Data Processing Agreement For the purposes of Article 28(3) of Regulation 2016/679 (the GDPR)1. Preamble1) These Contractual Clauses (the Clauses) set out the rights and obligations of the data controller and the data processor, when processing personal data on behalf of the data controller.2) The Clauses have been designed to ensure the parties’ compliance with Article 28(3) of Regulation 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data and repealing Directive 95/46/EC (General Data Protection Regulation). Appendix A Information about the processing A.1. The purpose of the data processor’s processing of personal data on behalf of the data controller is:Personal data will be processed on behalf of the Data Controller to deliver successful awareness training via an E-learning platform.A.2. The data processor’s processing of personal data on behalf of the data controller shall mainly pertain to (the nature of the processing): Appendix B Sub-processors The following table shows our vendors used to process personal data on behalf of the data controller.Name | Business ID. | Address | Purpose Appendix C Security Measures Risk ManagementRGPD.COM regularly assesses the risks to its systems and the personal data they process. This assessment is informed by the latest threat landscape and new industry insights, which shape our security measures and initiatives.Information Security PoliciesRGPD.COM follows an IT security policy, which is regularly reviewed to ensure compliance. Management approves the policy, which is communicated to all relevant employees and partners. It is reassessed regularly and whenever significant changes occur. Policy Privacy Policy ControllerWe are data controllers as we process the personal data of our customers and partners. You will find our contact information below.If you have questions about processing your data, you can contact us via mail@rgpd.com.Processing Activities Policy Cookie Policy This website does not set cookies and stores nothing on your device.You can learn more about how we process personal information in our privacy policy.