GDPR Risk Assessment Training
A GDPR risk assessment is an organised way to judge and lower risks to personal data. This training gives your colleagues a general understanding of how one works.
6 mins | 4 Lessons | 4 Quizzes
Get Started FreeWhat the training consists of
-
1. Introduction to risk assessments
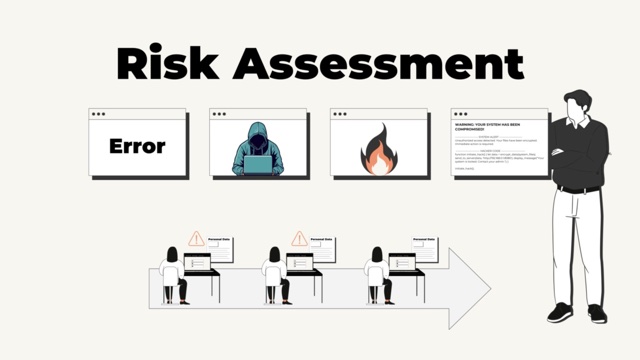
1:05A risk is anything that could harm the privacy and security of the personal data people work with. The first lesson explains how a risk assessment looks at each threat, asking how likely it is to happen and what it would mean for the people concerned.
-
2. What to assess and which threats to look for
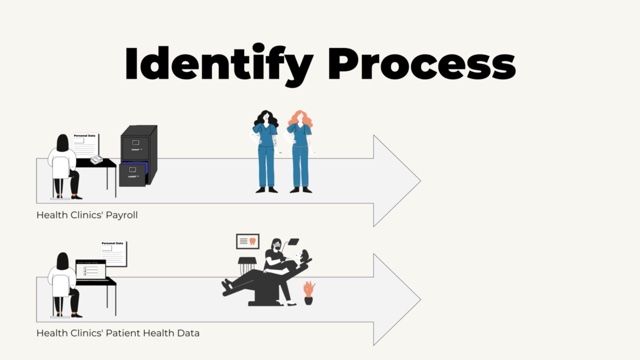
2:01An assessment starts with one processing activity, meaning one specific use of personal data. The second lesson shows how to choose it and the kinds of threats to look for, from technical failures and theft to cyber attacks and a breach at a supplier.
-
3. Likelihood and consequences
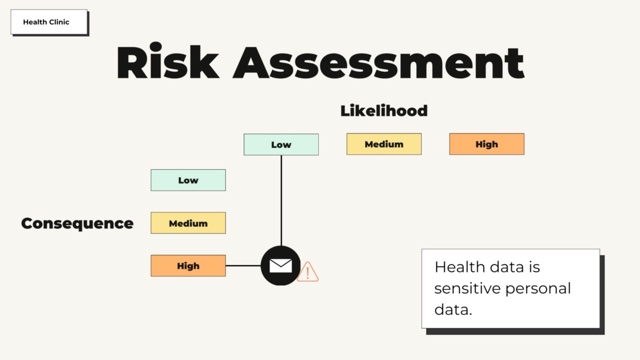
1:31The third lesson introduces a simple scoring method: each threat is rated low, medium or high, once for how likely it is and once for how serious the consequences would be. Using the same scale for every threat makes them easier to compare.
-
4. Risks and appropriate measures
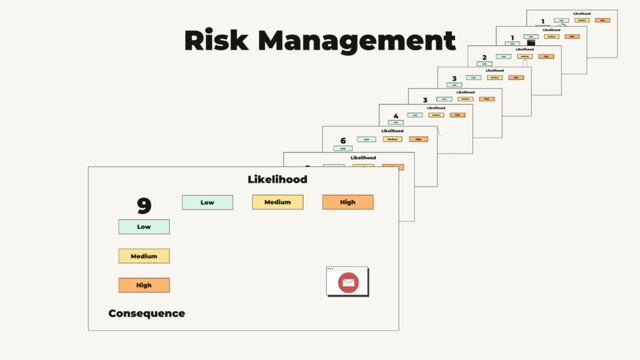
1:33The last lesson turns the two ratings into one risk score from 1 to 9: low, medium and high count as 1, 2 and 3, and the two are multiplied. With a score for every processing activity, the organisation can put its risks in order and deal with the highest first.
Why it matters
Risk assessments are a critical requirement under the GDPR. They show the organisation what it needs to do to protect personal data, so that its time, effort and resources are used wisely.
What your colleagues learn
- Each use of personal data has its own threats. A health clinic’s patient records in a cloud system face different threats from its staff files in a filing cabinet, so each one is assessed separately.
- Threats also come from inside the organisation. Employees mishandling data, misusing it on purpose or disposing of electronic devices improperly belong on the list alongside attacks from outside.
- A threat can be unlikely and still serious. Emailing health data to the wrong person by mistake is unlikely at a clinic that uses a patient portal instead of email, yet the harm would be high because health data is sensitive.
- A high risk is not always solved with technology. Lowering it can take a procedure for handling personal data, not only a technical measure.
Related Courses
View all →-
 GDPR & Security Practices
The GDPR expects personal data to be kept safe from the very first design of a system.
-
 Data Breaches
Spotting a personal data breach starts with knowing what one looks like.
-
 Information Security
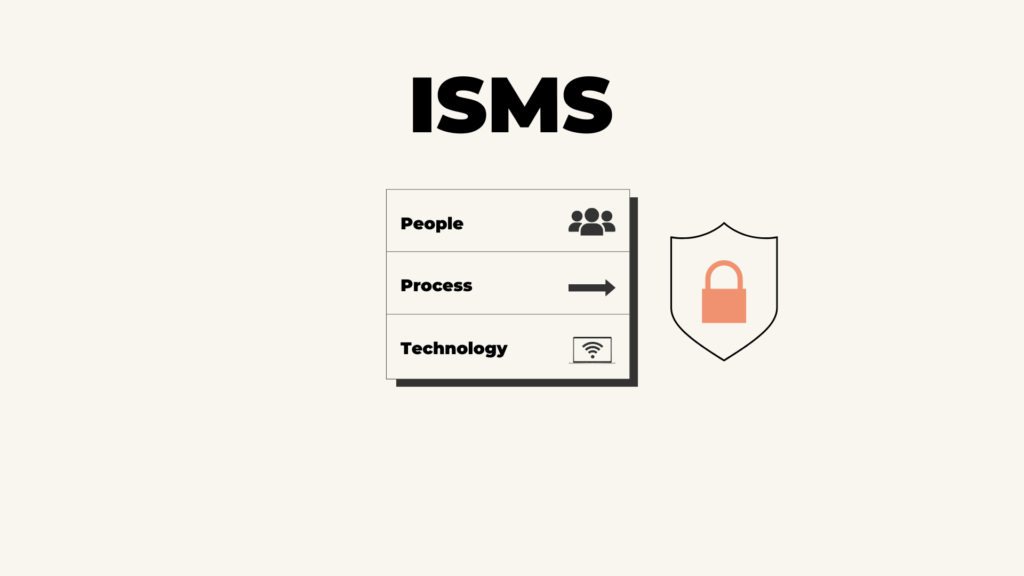
Protecting information is a task for the whole organisation, and every employee has a part in it.